
avoid-coinomi.com
46.62.252.5
Public Scan
Open in
urlscan Pro
http://avoid-coinomi.com/ 8yr old
Effective URL:
https://avoid-coinomi.com/ 8yr old
Submission Tags: phishdestroy
Submission: On March 12 via api (March 12th 2026, 12:39:53 pm UTC) from DE — Scanned from UK Go Pro
Only in urlscan Pro
- Select different country locations for Private Scans.
- Use a global network of additional scanning locations and residential IPs for scanning.
- Interact with pages while you are scanning them.
- Download files from remote websites.
- Scan websites on the Tor Network.
Summary
TLS certificate: Issued by R13 on February 2nd 2026. Valid for: 3mo.
This is the only time avoid-coinomi.com was scanned on urlscan.io!
urlscan.io Verdict: No classification
Live information
Domain & IP information
| IP Address | AS Autonomous System | ||
|---|---|---|---|
| 26 | 46.62.252.5 46.62.252.5 | 24940 (HETZNER-A...) (HETZNER-AS Hetzner Online GmbH) | |
| 1 | 64.233.166.95 64.233.166.95 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 1 | 142.251.141.78 142.251.141.78 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 3 | 142.251.39.99 142.251.39.99 | 15169 (GOOGLE) (GOOGLE - Google LLC) | |
| 34 | 5 |
ASN24940 (HETZNER-AS Hetzner Online GmbH, DE)
PTR: static.5.252.62.46.clients.your-server.de
| avoid-coinomi.com 8yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: wm-in-f95.1e100.net
| fonts.googleapis.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: tzfraa-ar-in-f14.1e100.net
| img.youtube.com 10yr old |
ASN15169 (GOOGLE - Google LLC, US)
PTR: pnpara-ag-in-f3.1e100.net
| fonts.gstatic.com 10yr old |
| Apex Domain Subdomains |
Transfer | |
|---|---|---|
| 26 |
avoid-coinomi.com
avoid-coinomi.com 8yr old |
1 MB |
| 3 |
gstatic.com
fonts.gstatic.com 10yr old |
75 KB |
| 1 |
youtube.com
img.youtube.com — Cisco Umbrella Rank: 1098 10yr old |
123 KB |
| 1 |
googleapis.com
fonts.googleapis.com — Cisco Umbrella Rank: 81 10yr old |
1 KB |
| 0 |
x.com
Failed
x.com Failed 14yr old |
|
| 34 | 5 |
| Domain | Requested by | |
|---|---|---|
| 26 | avoid-coinomi.com |
avoid-coinomi.com
|
| 3 | fonts.gstatic.com |
fonts.googleapis.com
|
| 1 | img.youtube.com |
avoid-coinomi.com
|
| 1 | fonts.googleapis.com |
avoid-coinomi.com
|
| 0 | x.com Failed |
avoid-coinomi.com
|
| 34 | 5 |
This site contains links to these domains. Also see Links.
| Subject Issuer | Validity | Valid | |
|---|---|---|---|
| avoid-coinomi.com R13 |
2026-02-02 - 2026-05-03 |
3mo | crt.sh |
| upload.video.google.com WR2 |
2026-02-02 - 2026-04-27 |
3mo | crt.sh |
| *.google.com WE2 |
2026-02-02 - 2026-04-27 |
3mo | crt.sh |
| *.gstatic.com WR2 |
2026-02-02 - 2026-04-27 |
3mo | crt.sh |
This page contains 1 frames:
Primary Page:
https://avoid-coinomi.com/
Frame ID: 4C0A87F464054A2C9FC5AD2F0B3367E0
Requests: 34 HTTP requests in this frame
Screenshot
Go Pro
Only in urlscan Pro
Use the Visual Search feature to find pages with visually similar screenshots.
Click for more information
Free trials of urlscan Pro are available.
Page Title
Coinomi Wallet Critical Vulnerability - 17 BTC (or its equivalent) Lost | Hidden Spell Check Security FlawPage URL History
Go Pro
Only in urlscan Pro
Search our real-time database of newly observed domains and
hostnames. Pivot on different attributes, and setup keyword alerts for
newly observed domains.
Click for more information
Free trials of urlscan Pro are available.
Show full URLs
-
http://avoid-coinomi.com/
HTTP 307
https://avoid-coinomi.com/ Page URL
Detected technologies
 YouTube
(Video players)
Expand
Detected patterns
- \.youtube\.com/
Page Statistics
100 Outgoing links
Go Pro
Only in urlscan Pro
Effortlessly use any on-page link as a pivot to discover other pages pointing to the exact same destination. Seamlessly trace both specific URLs and broader domains to uncover hidden connection networks and map out backlink relationships with ease.
Click for more information
Free trials of urlscan Pro are available.
These are links going to different origins than the main page.
Title: CipherBlade
Search URL Search Domain Scan URL
Title: ▶ Watch on YouTube
Search URL Search Domain Scan URL
Title: Coinomi
Search URL Search Domain Scan URL
Title: ShapeShift
Search URL Search Domain Scan URL
Title: amy_castor_article.html
Search URL Search Domain Scan URL
Title: decrypt_article.html
Search URL Search Domain Scan URL
Title: david_gerard_article.html
Search URL Search Domain Scan URL
Title: Exodus
Search URL Search Domain Scan URL
Title: Twitter
Search URL Search Domain Scan URL
Title: @warith2020
Search URL Search Domain Scan URL
Title: chrome_dict_en-us-8-0.bdic
Search URL Search Domain Scan URL
Title: Google
Search URL Search Domain Scan URL
Title: View JxBrowser Documentation
Search URL Search Domain Scan URL
Title: coinomi_statement_2019.html
Search URL Search Domain Scan URL
Title: chromium_spell_checker_docs.html
Search URL Search Domain Scan URL
Title: BitsonLine Article
Search URL Search Domain Scan URL
Title: Luke Childs' Blog Post
Search URL Search Domain Scan URL
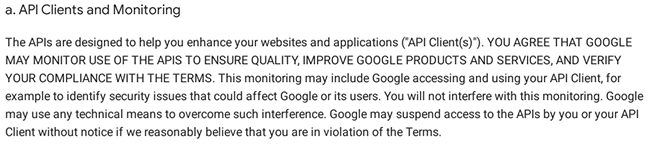
Title: google_dev_terms.html
Search URL Search Domain Scan URL
Title: google_api_data_policy.html
Search URL Search Domain Scan URL
Title: View the USPTO Trademark Filing
Search URL Search Domain Scan URL
Title: Reddit
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Search URL Search Domain Scan URL
Title: cipherblade_report.html
Search URL Search Domain Scan URL
Title: cipherblade_shapeshift_defense.html
Search URL Search Domain Scan URL
Title: Chainalysis
Search URL Search Domain Scan URL
Title: arstechnica_backdoor_report.html
Search URL Search Domain Scan URL
Title: original_tweet_link.html
Search URL Search Domain Scan URL
Title: spyshelter_clipboard_protection.html
Search URL Search Domain Scan URL
Title: PayPal
Search URL Search Domain Scan URL
Title: Amazon
Search URL Search Domain Scan URL
Title: eBay
Search URL Search Domain Scan URL
Title: cipherblade_incorporation_docs.html
Search URL Search Domain Scan URL
Title: seychelles_money_laundering_report.html
Search URL Search Domain Scan URL
Title: https://teamdev.com/jxbrowser/docs/guides/spell-checker/
Search URL Search Domain Scan URL
Title: https://teamdev.com/jxbrowser/docs/guides/chromium/
Search URL Search Domain Scan URL
Title: https://www.reddit.com/r/Bitcoin/comments/av987o/security_vulnerability_coinomi_wallet_sends_your/
Search URL Search Domain Scan URL
Title: @aseiberg66 Post 1
Search URL Search Domain Scan URL
Title: @aseiberg66 Post 2
Search URL Search Domain Scan URL
Title: @aseiberg66 Post 3
Search URL Search Domain Scan URL
Title: @aseiberg66 Post 4
Search URL Search Domain Scan URL
Title: @aseiberg66 Post 5
Search URL Search Domain Scan URL
Title: @aseiberg66 Post 6
Search URL Search Domain Scan URL
Title: @aseiberg66 Post 7
Search URL Search Domain Scan URL
Title: @aseiberg66 Post 8
Search URL Search Domain Scan URL
Title: @aseiberg66 Post 9
Search URL Search Domain Scan URL
Title: @lebblionsoh Post 1
Search URL Search Domain Scan URL
Title: @lebblionsoh Post 2
Search URL Search Domain Scan URL
Title: @lebblionsoh Post 3
Search URL Search Domain Scan URL
Title: @lebblionsoh Post 4
Search URL Search Domain Scan URL
Title: @lebblionsoh Post 5
Search URL Search Domain Scan URL
Title: @lebblionsoh Post 6
Search URL Search Domain Scan URL
Title: @lebblionsoh Post 7
Search URL Search Domain Scan URL
Title: @lebblionsoh Post 8
Search URL Search Domain Scan URL
Title: @lebblionsoh Post 9
Search URL Search Domain Scan URL
Title: @hendraalhendra Post 1
Search URL Search Domain Scan URL
Title: @hendraalhendra Post 2
Search URL Search Domain Scan URL
Title: @hendraalhendra Post 3
Search URL Search Domain Scan URL
Title: @apedrera Report
Search URL Search Domain Scan URL
Title: @shamanater Report
Search URL Search Domain Scan URL
Title: @ScottRoger44047 Post 1
Search URL Search Domain Scan URL
Title: @ScottRoger44047 Post 2
Search URL Search Domain Scan URL
Title: @mrwaltertaylor Report
Search URL Search Domain Scan URL
Title: @RoyHernandez100 Report
Search URL Search Domain Scan URL
Title: @ShaneNe59564115 Post 1
Search URL Search Domain Scan URL
Title: @ShaneNe59564115 Post 2
Search URL Search Domain Scan URL
Title: @ShaneNe59564115 Post 3
Search URL Search Domain Scan URL
Title: @HelenRattigan4 Report
Search URL Search Domain Scan URL
Title: @SaeeDJooN2 Report
Search URL Search Domain Scan URL
Title: @hopeseekr Report
Search URL Search Domain Scan URL
Title: @Mbulawa16 Report
Search URL Search Domain Scan URL
Title: @seanfulop Report
Search URL Search Domain Scan URL
Title: @MrLewisStephen1 Report
Search URL Search Domain Scan URL
Title: @ambitiousjuliet Report
Search URL Search Domain Scan URL
Title: @gatekeepr Report
Search URL Search Domain Scan URL
Title: @BlanqueroJesus Report
Search URL Search Domain Scan URL
Title: @fuckeverycrypto Report
Search URL Search Domain Scan URL
Title: @99kTrades Report
Search URL Search Domain Scan URL
Title: @XRPsoon Report
Search URL Search Domain Scan URL
Title: @CryptoYoda1338 Report
Search URL Search Domain Scan URL
Title: @VainilaMarket Report
Search URL Search Domain Scan URL
Title: @papacapt Report
Search URL Search Domain Scan URL
Title: @moderninvestor Report
Search URL Search Domain Scan URL
Title: @Avoid_coinomi
Search URL Search Domain Scan URL
Title: I get hacked, 2.4 BTC stolen from Coinomi wallet (Android)
Search URL Search Domain Scan URL
Title: I get hacked, 2.4 BTC stolen from Coinomi wallet
Search URL Search Domain Scan URL
Title: Coinomi wallet hacked, all funds stolen
Search URL Search Domain Scan URL
Page URL History
This captures the URL locations of the websites, including HTTP redirects and client-side redirects via JavaScript or Meta fields.
-
http://avoid-coinomi.com/
HTTP 307
https://avoid-coinomi.com/ Page URL
Redirected requests
There were HTTP redirect chains for the following requests:
34 HTTP transactions
Go Pro
Only in urlscan Pro
Inspect WebSocket connections, examine POST data effortlessly, and track overlap counts in real time. Features live search and filtering across all HTTP output, complete with full response metadata for deep analysis.
Click for more information
Free trials of urlscan Pro are available.
0 data transactions
| Method Protocol |
Status | Resource Path |
Size x-fer |
Time Latency |
Type MIME-Type |
IP Location |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
GET H2 |
200 |
Primary Request
/
Show response
avoid-coinomi.com/ Redirect Chain
|
240 KB 54 KB |
423ms
161ms |
Document
text/html |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
Redirect headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
css2
fonts.googleapis.com/ |
16 KB 1 KB |
201ms
83ms |
Stylesheet
text/css |
64.233.166.95 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
maxresdefault.jpg
img.youtube.com/vi/eP1WAkTJXw0/ |
123 KB 123 KB |
282ms
95ms |
Image
image/jpeg |
142.251.141.78 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
coinomi_screenshot_1.png
avoid-coinomi.com/files/ |
58 KB 58 KB |
133ms
133ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
coinomi_quote_1.png
avoid-coinomi.com/files/ |
13 KB 13 KB |
104ms
101ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
coinomi_quote_2.png
avoid-coinomi.com/files/ |
50 KB 50 KB |
151ms
148ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
coinomi_quote_3.png
avoid-coinomi.com/files/ |
83 KB 83 KB |
153ms
151ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
coinomi_quote_4.png
avoid-coinomi.com/files/ |
58 KB 58 KB |
153ms
150ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
google_terms_1.png
avoid-coinomi.com/files/ |
41 KB 41 KB |
153ms
151ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
google_terms_2.png
avoid-coinomi.com/files/ |
75 KB 75 KB |
236ms
234ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
google_terms_3.png
avoid-coinomi.com/files/ |
48 KB 48 KB |
237ms
235ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
coinomi_ceo_founder.png
avoid-coinomi.com/files/ |
48 KB 48 KB |
237ms
234ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
profile_image
x.com/kimonis/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
john_jegutanis_coinomi.jpg
avoid-coinomi.com/files/ |
3 KB 3 KB |
237ms
235ms |
Image
text/html |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
profile_image
x.com/angelitto_ffs/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET |
|
profile_image
x.com/KobyLazar/ |
0 0 |
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
vasilis_perlis_coinomi.jpg
avoid-coinomi.com/files/ |
3 KB 3 KB |
236ms
235ms |
Image
text/html |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
dimitris_katsinelos_coinomi.jpg
avoid-coinomi.com/files/ |
3 KB 3 KB |
236ms
235ms |
Image
text/html |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
404 |
coinomi_company_logo.png
avoid-coinomi.com/files/ |
3 KB 3 KB |
265ms
264ms |
Image
text/html |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
coinomi_support_ticket_google.png
avoid-coinomi.com/files/ |
13 KB 13 KB |
276ms
275ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
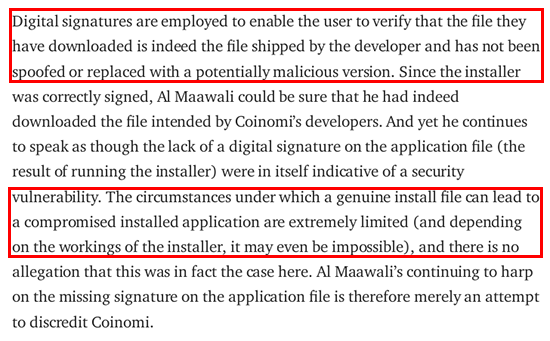
cipherblade_quote_8.png
avoid-coinomi.com/files/ |
21 KB 21 KB |
278ms
277ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
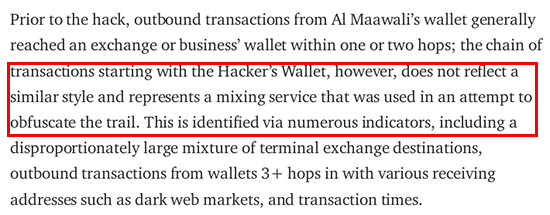
cipherblade_quote_1.png
avoid-coinomi.com/files/ |
87 KB 87 KB |
267ms
266ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
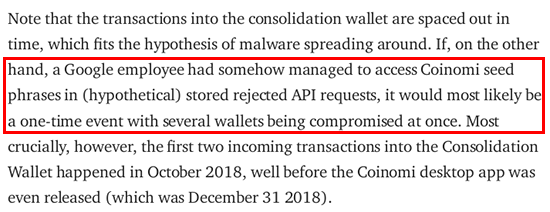
cipherblade_quote_2.png
avoid-coinomi.com/files/ |
91 KB 91 KB |
278ms
278ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cipherblade_quote_3.png
avoid-coinomi.com/files/ |
66 KB 66 KB |
266ms
264ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cipherblade_quote_4.png
avoid-coinomi.com/files/ |
35 KB 35 KB |
266ms
265ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cipherblade_quote_5.png
avoid-coinomi.com/files/ |
57 KB 57 KB |
266ms
265ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
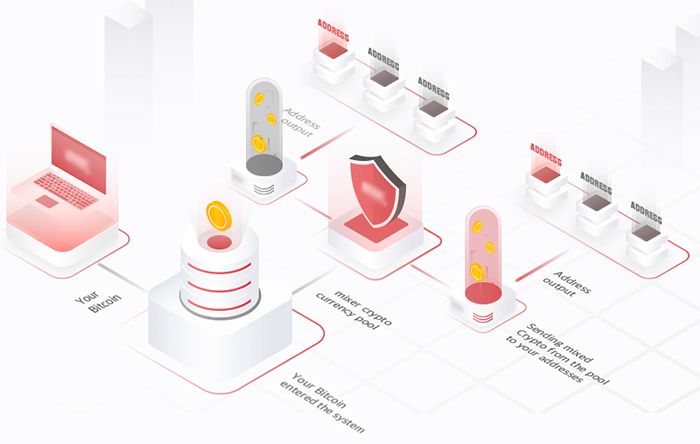
mixer.png
avoid-coinomi.com/files/ |
164 KB 164 KB |
266ms
265ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cipherblade_quote_7.png
avoid-coinomi.com/files/ |
54 KB 54 KB |
266ms
265ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cipherblade_quote_6.png
avoid-coinomi.com/files/ |
55 KB 55 KB |
266ms
265ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
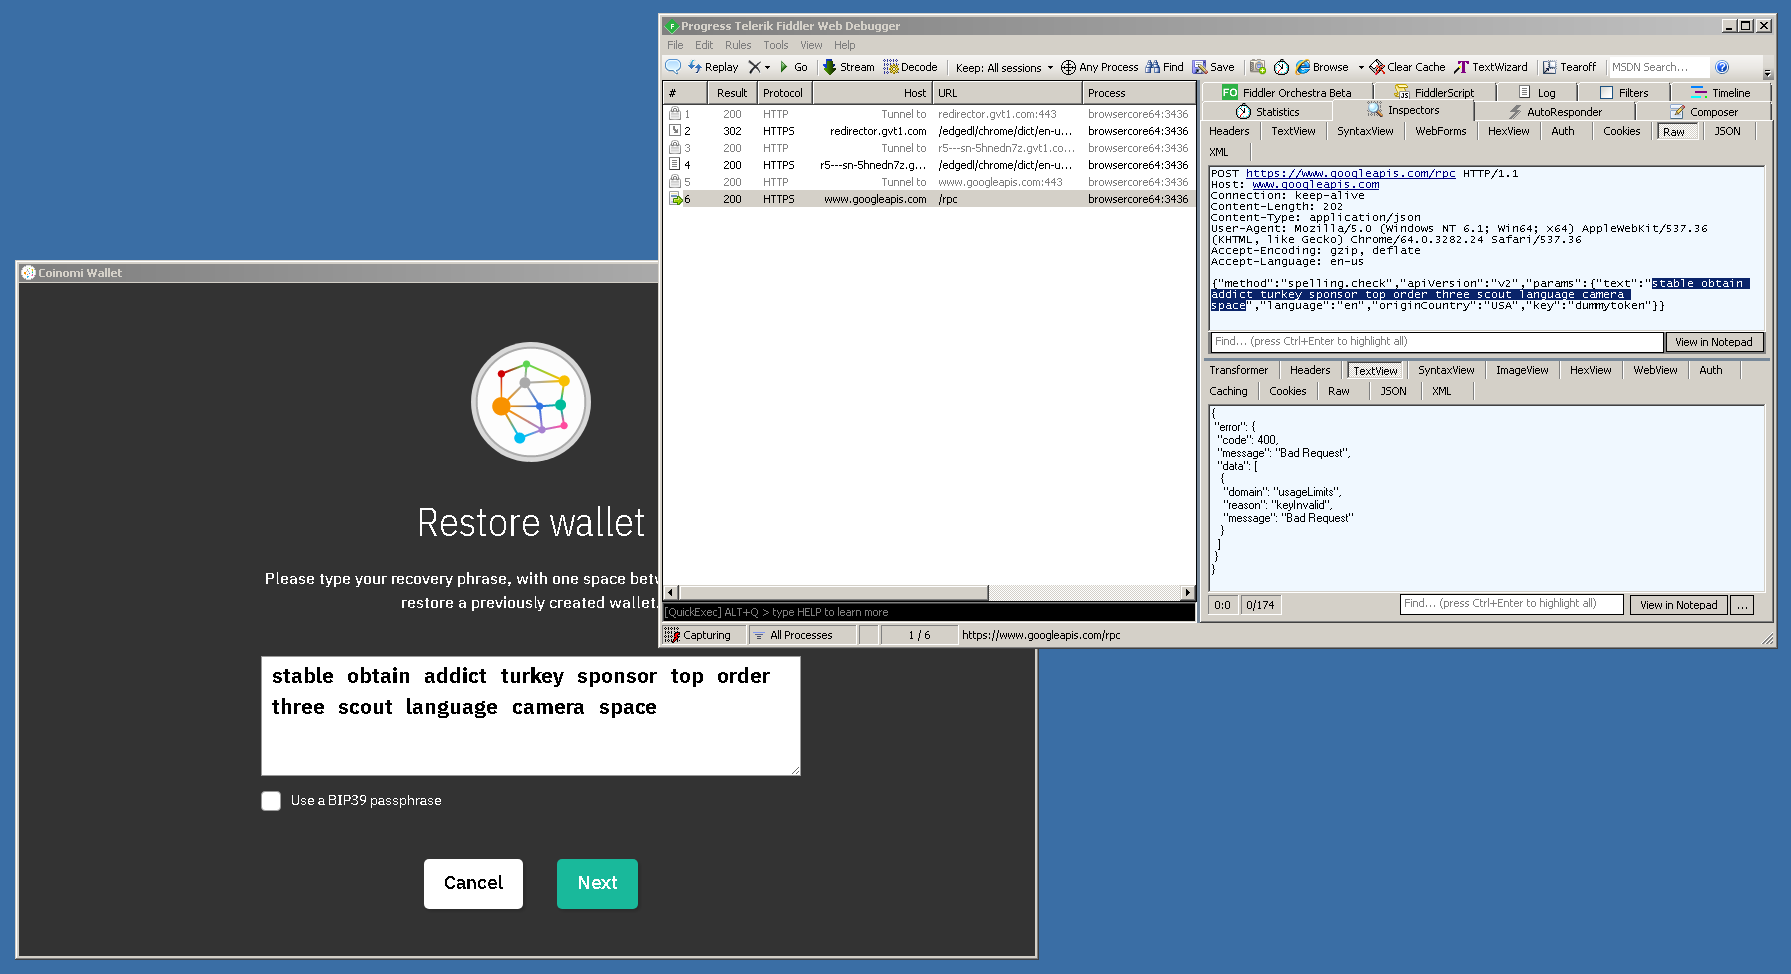
cipherblade_screenshot_1.png
avoid-coinomi.com/files/ |
61 KB 61 KB |
266ms
266ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H2 |
200 |
cipherblade_screenshot_2.png
avoid-coinomi.com/files/ |
22 KB 22 KB |
266ms
266ms |
Image
image/png |
46.62.252.5 HETZNER-AS Hetzne... |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
UcC73FwrK3iLTeHuS_nVMrMxCp50SjIa1ZL7W0Q5nw.woff2
fonts.gstatic.com/s/inter/v20/ |
47 KB 47 KB |
126ms
63ms |
Font
font/woff2 |
142.251.39.99 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
S6u9w4BMUTPHh6UVSwiPGQ3q5d0.woff2
fonts.gstatic.com/s/lato/v25/ |
14 KB 14 KB |
120ms
58ms |
Font
font/woff2 |
142.251.39.99 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
|
GET H3 |
200 |
S6uyw4BMUTPHjx4wXiWtFCc.woff2
fonts.gstatic.com/s/lato/v25/ |
14 KB 14 KB |
147ms
85ms |
Font
font/woff2 |
142.251.39.99 Google LLC |
|||||||||||||||||||||||||||||||||||||||||||||||||||||
|
General
Request headers
Response headers
|
|||||||||||||||||||||||||||||||||||||||||||||||||||||||||||










































Failed requests
These URLs were requested, but there was no response received. You will also see them in the list above.
- Domain
- x.com
- URL
- https://x.com/kimonis/profile_image?size=original
- Domain
- x.com
- URL
- https://x.com/angelitto_ffs/profile_image?size=original
- Domain
- x.com
- URL
- https://x.com/KobyLazar/profile_image?size=original
Verdicts & Comments Add Verdict or Comment
2 JavaScript Window variables
Go Pro
Only in urlscan Pro
Inspect and pivot on JavaScript variables, identifiers, and other key site metadata data with urlscan Pro. Reveal and search on client-side frameworks, runtime variables, and custom values.
Click for more information
Free trials of urlscan Pro are available.
These are the non-standard variables defined on the window object. These include var declarations and global functions and can be helpful in identifying possible client-side frameworks and code.
function| openLightbox function| closeLightbox1 Cookies
Go Pro
Only in urlscan Pro
Review, search, and pivot on browser cookies and persistence site data to see how a site tracks users and keeps sessions alive across visits.
Click for more information
Free trials of urlscan Pro are available.
Cookies are little pieces of information stored in the browser of a user. Whenever a user visits the site again, he will also send his cookie values, thus allowing the website to re-identify him even if he changed locations. This is how permanent logins work.
| Domain/Path | Expires | Name / Value | |||
|---|---|---|---|---|---|
| .x.com/ | 1970-01-21 22:05:33 |
Name: guest_id Value: v1%3A177331919457971562 |
4 Console Messages
A page may trigger messages to the console to be logged. These are often error messages about being unable to load a resource or execute a piece of JavaScript. Sometimes they also provide insight into the technology behind a website.
| Source | Level | URL Text |
|---|
Indicators
This is a term in the security industry to describe indicators such as IPs, Domains, Hashes, etc. This does not imply that any of these indicate malicious activity.
avoid-coinomi.com
fonts.googleapis.com
fonts.gstatic.com
img.youtube.com
x.com
x.com
142.251.141.78
142.251.39.99
46.62.252.5
64.233.166.95
064764e5dc4b0930a623d65c6af4fd7a28f987ada280ae3257a9a815d41da7b2
3103168e48460486a8cb090c893d937d8fae2b5cf01eb09f61dc8ca1bc016225
35bd9c3ac4b97c9f7787f13fbc231932a7729d57b4ed989b6d192a6a2d8ee97d
37b704018b97271f8ea5d36c392a7c6af34b1f7fabce4282aa2562d95ad155af
4308668ead371902d6b9f604b1e41436a0b50853b33386d59354fed3bb50ca0d
49f4085c0c683d30920ad14a3c243c4587725cb7a3bb179f3f14e4463a501281
50bfe3cfbea0aef4dc3330a502ab05c4cffb5bb584c8bfc8d5e47868f343a533
72df73425f7ba6680edb366ed7b9e566c2f3f1b44f769cbd6f41801b56d362f7
7a7ce1a34f3e9944fe88fc61abbc93b6db383afa2b90815fd7ccea456fbce4e5
98ae3e7d3b67d27053b40ce2e72416cf8770d7c3a1f7fec0df7197fdbdbdadc6
9e6158e31644cfd2a771d0a266122341a511ee87bbedd7b35ba2bbf106a06fe1
9fc4452ccd6a603e45f61a0b6669dda46fe96afe0a08200ad71bc1c787b5f0c4
a247c7abf494b2c533503b477b23c0cc6b2f144f15308ca95d36a75c294953b6
a59908877a8cacc5fdd5e59a8fe70c72a418195f18bf7900b025664bbb0b38da
a5ec9f34d6062f83d3f6675641418ed86976df71a8e249740c0d26501535f5b0
a80a04b4adcef027e6574d1a77cb3a456cf8affe8f04d6d2e9d7f5637317b998
a848174c85320019774dc65395d71b0fc64cbf3e5b21acc05fbb907405508c8b
c23e8501276a9801b3b1c635b6a12398f84054d9cddc2f77688146f8455bfc7c
c940764593d0fe5d596be327ca7558855e018039fb78509aa21921fd3644c3e4
cae315166fd87d116ef9e92751ef6506b15480ce06097f89ce4b42715d98cbd2
d4ae5188a65370ecfe28f42293bbee8297cfd5712c6aadfdb270d48f2bcd88b0
de7542e397006ca0ee8b93aceff47f248fdfaf91f4dec51bff8df24a58c0b9a3
df96d8a15c58c66e761b9a3258b4569a5a28be384cd558907cc467ce1806ef8c
e2535d411b42bca1b06e8ab2917bd34f758017f982b84a08579659272bf7d1b0
e4b66b2369b0685577aedbc542b45cad3d09e5ffb05c28b72a603740bdbbe092
e89f65c33c3d34b8c2eb6edd6609ed77ed79c9afe47d4aead4aaba844b781f28
ebb952b40aad1744775905b0e0765657920229c33f516d97d13f8f9d56fb84e6
ecf18fa0a691e0c1e2ca53e3bd609d84a8f4c74500b2523d449d00b999ff7a1e